

About Single Sign-On
Single sign-on (SSO) in Iru Endpoint lets team members log in to the Iru Endpoint web app using their existing identity provider credentials, providing centralized authentication management.How It Works
Team Members have four options for logging into the Iru Endpoint Web App: Passkeys, Google Social, Microsoft Social and Single Sign-On (SSO). By default, Passkeys, Google Social, and Microsoft Social authentication are activated for all tenants, offering login through Passkeys, Google Social, and Microsoft Social. Admins have the option to enable SSO using either native integrations or Custom SAML. Once an SSO setup is complete, the default connections can be turned off, allowing SSO to be the only login method. SSO can also be used for Require Authentication for Enrollment.SSO Connection Types
Iru Endpoint currently supports the following Single Sign-On connection types. Select one of the following connection types to learn how it can be configured.- Single Sign-On with Microsoft Entra ID (Native)
- Single Sign-On with Microsoft Entra ID (SAML)
- Single Sign-On with Google Workspace (Native)
- Single Sign-On with Google Workspace (SAML)
- Single Sign-On with Okta (SAML)
- Single Sign-On with JumpCloud (SAML)
- Single Sign-On with OneLogin (SAML)
- Custom SAML-based Single Sign-On
Allowing Tenant Authentication and Managing Connections
Once you have configured an SSO connection in both Iru Endpoint and your identity provider (IdP), you can allow the SSO connection to be used for tenant authentication.1
Access Connection Menu
Select the ellipsis next to the connection name.
2
Allow for Tenant Authentication
Select Allow for tenant authentication from the menu. Connections can also be re-configured, deleted, and disabled from this menu.
Considerations for Allowing Tenant Authentication
- An SSO connection does not need to be allowed for tenant authentication to be used for Require Authentication during Device Enrollment.
- A connection should only be set to Allow tenant authentication in Access if you want to authenticate Iru Endpoint administrators to the web app with that connection.
- Authentication to the Iru Endpoint Web App using SSO requires that the user has been invited as a Team Member.
Allow for Tenant Authentication
Once you have configured the SAML connection in Iru Endpoint and your identity provider, you can allow its use for tenant authentication. For step-by-step instructions, please refer to the Allowing Tenant Authentication and Managing Connections section in our Single Sign-on support article.Limit Authentication to Domain
When configuring the SAML connection, you can optionally limit authentication to one or more domains. This can be useful when the SSO connection could authenticate to multiple domains. You can limit the authentication to your Iru tenant to a subset of the available domains.Enforcing Single Sign-On
Once you have configured at least one Single Sign-on connection, you can disable Passkey, Google Social, and Microsoft Social connections. Disabling these connections will disable the ability for Iru Endpoint administrators in your tenant to authenticate via those methods. Please refer to our Single Sign-on support article for step-by-step instructions.1
Navigate to the Account Menu Button
In Iru Endpoint, in the sidebar, select the Account Menu Button.
2
Access Authentication Settings
Select the Access option in the menu.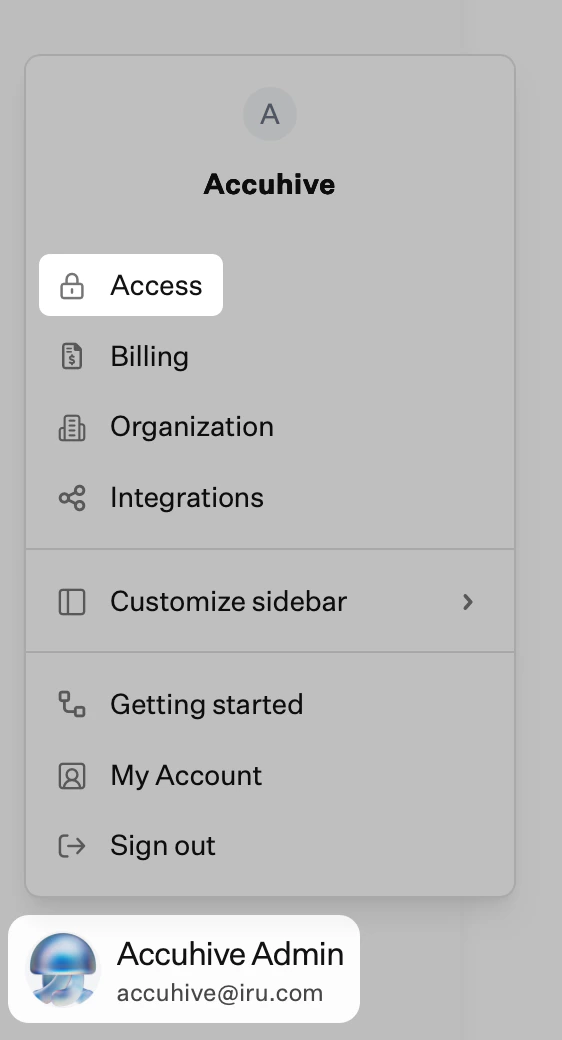
3
Connection Menu
Select the ellipsis next to Passkey.
4
Disable for Passkey Tenant Authentication
Select Disable for tenant authentication
5
Disable Social Tenant Authentication
Repeat the previous steps for the Google Social and Microsoft Social connections.
If you lose access to your Iru Endpoint tenant via SSO and need to have Passkey, Google Social, or Microsoft Social connections re-enabled, please contact Iru Endpoint support.
Disabling or Deleting SSO Connections
If you decide to stop using SSO, you can delete it or disable it for tenant authentication using the same ellipsis used to enable it. When there is only one SSO connection enabled for tenant authentication, and Passkey, Google Social, and Microsoft Social are disabled, you will not be able to disable that SSO connection to prevent tenant lockout. You would first need to enable another connection, and authentication with that other connection before disabling the SSO connection.Best Practices
Testing: Always test your SSO connection thoroughly before disabling Passkey, Google Social, and Microsoft Social connections to prevent tenant lockout. User Management: Ensure all necessary users have been invited as Team Members before relying solely on SSO authentication. Backup Access: Keep at least one of the Passkey, Google Social, or Microsoft Social connections enabled until you’re confident your SSO setup is working correctly for all users. Support: If you encounter issues with an SSO connection, Passkey, Google Social, or Microsoft Social connections can be re-enabled by contacting Iru Endpoint support.Related Articles
Team Member Role Permissions
Reference guide for Iru team member roles and permissions. Compare access levels for Account Owner, Admin, Standard, Help Desk, Auditor, and more.
Admins and Access
Add team members to Iru Endpoint and set role-based access. Assign administrator, standard, help desk, or auditor levels to control permissions.
Configure Require Authentication for Enrollment
Require user authentication during device enrollment in Iru Endpoint. Configure identity verification for Apple, Windows, and Android platforms.
Single Sign-on with Microsoft Entra ID (Native)
Configure native Microsoft Entra ID SSO for Iru Endpoint using OAuth2 and OpenID Connect. Enable one-click sign-in for admins with Microsoft Entra ID credentials.