

This guide applies to Mac computers, iOS devices, and iPadOS devices
Be sure to have the appropriate prerequisites in place before starting the MSDC integration setup. See Getting Started with Microsoft Device Compliance for the Microsoft Device Compliance setup path diagram and rollout order.
Configuring the MSDC Integration in Iru Endpoint
1
Open Integrations
In the sidebar, select the Account Menu Button, then select Integrations.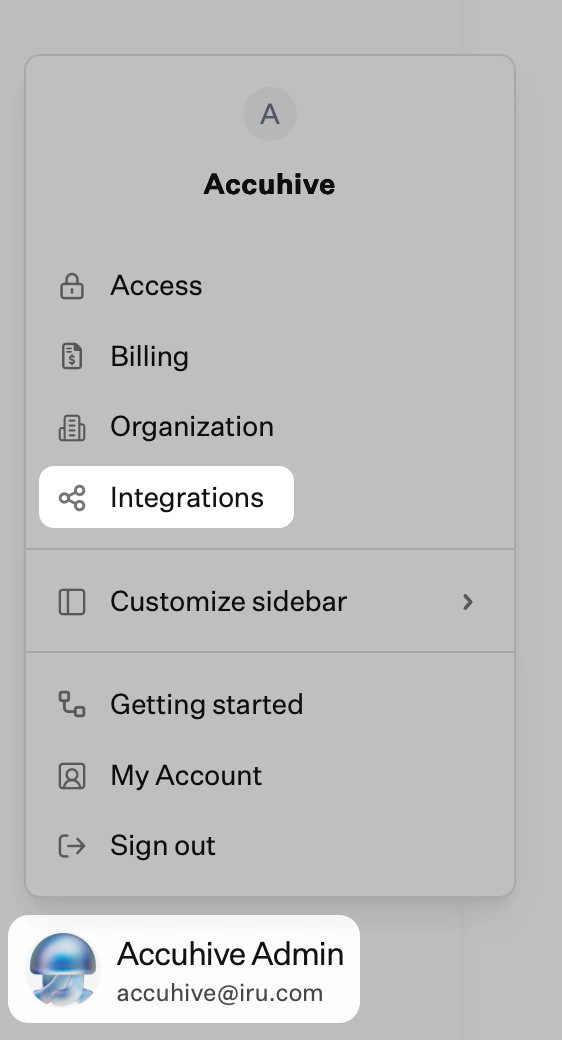
2
Browse all integrations
Select Browse all integrations in the upper-right of the Integrations page.
3
Select Microsoft Device Compliance
Select the Microsoft Device Compliance tile.
4
Review Prerequisites
Review the Prerequisites and select Next.
5
Enter Domain and Sign In
Enter your Microsoft primary domain URL on the next page and select Sign in with Microsoft.
6
Accept Permissions
Follow the Microsoft OAuth prompts and Accept the permissions requested by the Iru Endpoint Device Compliance enterprise app.
7
Select Device Platforms and User Groups
On the Device platforms page, select the device platforms and appropriate Microsoft user groups that will be in scope for device compliance. The selected platforms and user groups should match what was configured in Intune when adding Iru Endpoint as a device compliance partner.
8
Complete Setup
Select Next to complete the initial setup.
Deleting the MSDC Integration from Iru Endpoint
Complete the following steps to delete the MSDC integration from your Iru Endpoint tenant:1
Open Integrations
In the sidebar, select the Account Menu Button, then select Integrations. Locate the Microsoft Device Compliance integration.
2
Access Action Menu
Select the Action menu.
3
Select Delete Integration
Select Delete Integration.
4
Confirm Deletion
In the modal that appears, review the provided information and select Delete Integration.
Next Steps
After the MSDC integration is connected in Iru Endpoint:1
Deploy SSO Profiles and Registration Apps
Complete Microsoft Device Compliance: Library Item Configuration for Single Sign-on profiles, the Microsoft Company Portal Auto App (macOS), or Authenticator and Self Service (iOS and iPadOS). Deploy Single Sign-on profiles first if they are not already in place. See Single Sign-on Profiles.