

This guide applies to Mac computers and Windows computers
About Malware Detection Testing
The EICAR (European Institute for Computer Anti-Virus Research) test file provides a safe, standardized way to validate that Iru Endpoint EDR is deployed correctly. The EICAR test file is non-malicious and designed to trigger anti-malware systems without posing a security risk. For more information, visit EICAR’s Anti-Malware Test File page.How It Works
Malware detection testing using the EICAR test file validates that Iru Endpoint EDR is functioning correctly on enrolled devices. The test file triggers file-based detection in both Detect and Protect posture modes, allowing you to confirm reporting and quarantine behavior.Prerequisites
- EDR Library Item deployment: Confirm the EDR Library Item has been applied to the device. A green dot should appear next to the EDR Library Item in the Status tab of the Device Record.
- macOS
- Windows
Create the EICAR Test File
Option 1: Download Using Terminal
1
Open Terminal
Open Terminal.
2
Download EICAR File
Run the following command to download the EICAR test file directly from EICAR onto your Desktop:
Option 2: Manually Build the EICAR Test File
1
Create Text File
Create a new empty text file using a text editor such as VS Code or Sublime Text.
You can also use TextEdit, but you will need to set it to use plain text format. Choose Format > Make Plain Text, or press Shift-Command-T, so the file stays plain text before you add the EICAR string.
2
Add EICAR String
Copy and paste the following string into the text file:
3
Save File
Save the text file to the Desktop on your Mac and name the file eicar_test.
Expected Results
In Detect mode, Iru Endpoint EDR detects the EICAR test file and reports it with a status of Not quarantined on the Detections page (under Endpoint in the left-hand navigation) and in the Detections tab of the Device Record.In Protect mode, Iru Endpoint EDR detects and automatically quarantines the EICAR test file within seconds of making the file executable (for example, runchmod +x ~/Desktop/eicar_test). On the Detections page and in the Detections tab of the Device Record, Threat status shows Remediated, and Quarantined on shows when the file was quarantined.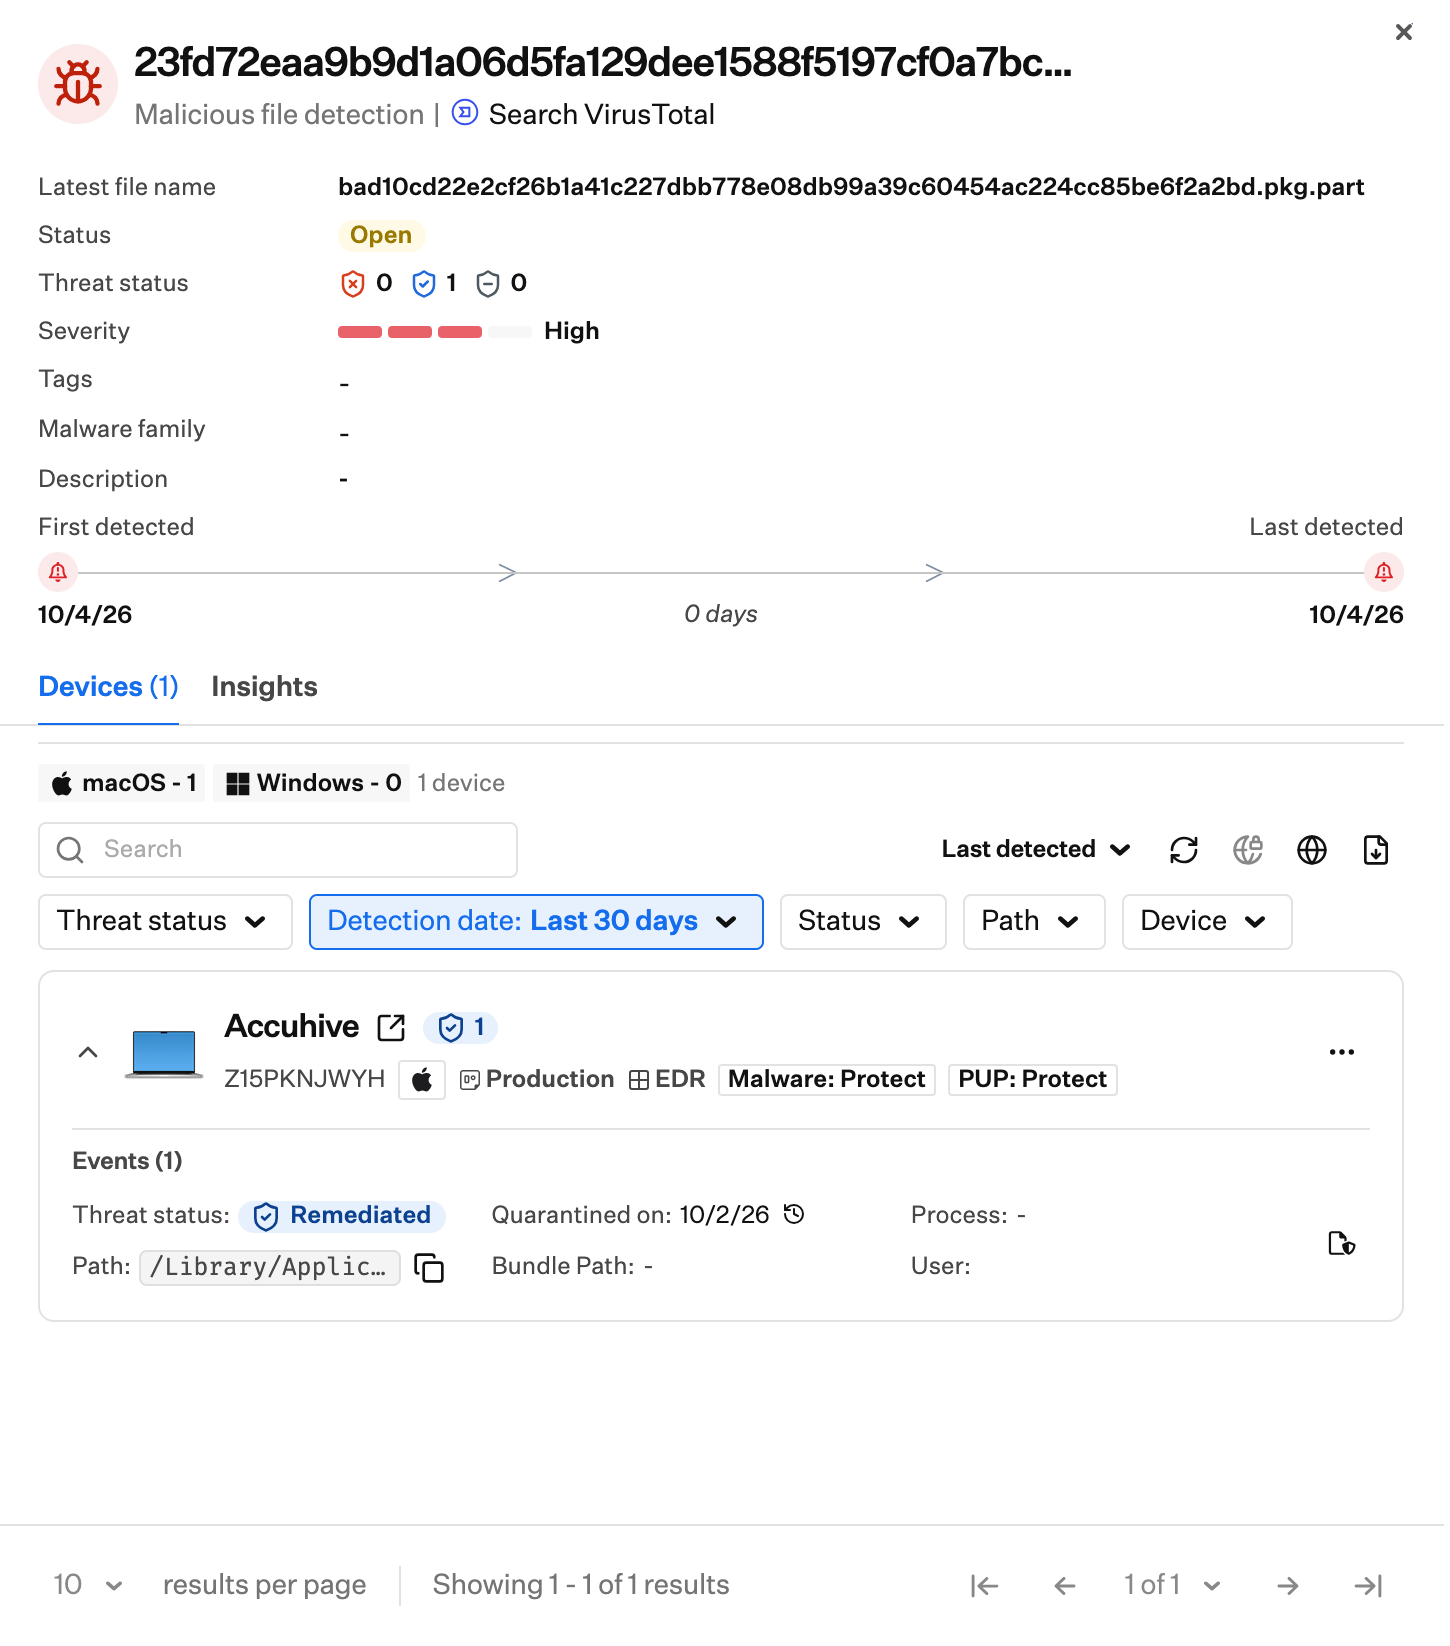
The 68-character EICAR string is the standard Anti-Malware Test File contents.
Considerations
- Safe testing: The EICAR test file is completely safe and designed specifically for anti-malware validation
- Posture mode testing: Test both Detect and Protect modes to confirm your EDR Library Item settings
- Status verification: Verify threat status in both the Detections module and individual device records
- macOS Protect mode: Quarantine occurs after the EICAR file is made executable
- Microsoft Defender Antivirus: Account for Microsoft Defender Antivirus behavior when interpreting test results on Windows computers
- Regular testing: Include EICAR testing in periodic security validation procedures
- Documentation: Record test results as part of compliance and audit documentation
Related Articles
Configure the EDR Library Item
Set Malware Response and PUP Response before you test
Endpoint Detection & Response (EDR) Overview
Review EDR capabilities for Mac and Windows
Understanding the Detections Page
Find the EICAR detection on the Detections page
Testing EDR behavioral detections
Validate behavioral detection in Detect and Protect